CISA adds SharePoint code-injection CVE with a September 28 deadline


CISA added CVE-2026-65660 in Microsoft SharePoint to its Known Exploited Vulnerabilities catalog on September 25, giving covered federal agencies until September 28 to apply vendor guidance.
Microsoft SharePoint administrators have a short remediation window for CVE-2026-65660. CISA added the vulnerability to its Known Exploited Vulnerabilities catalog on September 25, 2026, and lists September 28 as the due date for agencies covered by its federal remediation guidance.
What CISA says about CVE-2026-65660
CISA describes CVE-2026-65660 as a Microsoft SharePoint code-injection vulnerability. Its catalog entry says an authorized attacker could execute code over a network. The entry is a known-exploitation signal, not a severity score or a complete deployment assessment: administrators still need Microsoft’s advisory and their own asset inventory to determine exposure.
The deadline is especially relevant for internet-facing or business-critical SharePoint deployments. CISA’s catalog requires federal civilian agencies to apply vendor instructions under the applicable binding operational directive, or to discontinue use when mitigation is unavailable. Organizations outside that scope are not automatically subject to the federal deadline, but the catalog entry is a strong reason to treat the update as urgent.
Microsoft’s advisory is the remediation source
Microsoft’s Security Response Center tracks the vulnerability at its official Security Update Guide entry. Use that page to identify the affected SharePoint versions, fixed builds, installation sequence, and any deployment-specific workarounds. Do not rely on a generic Windows patching cycle: SharePoint farms often require coordination across servers, search, authentication, customizations, and rollback planning.
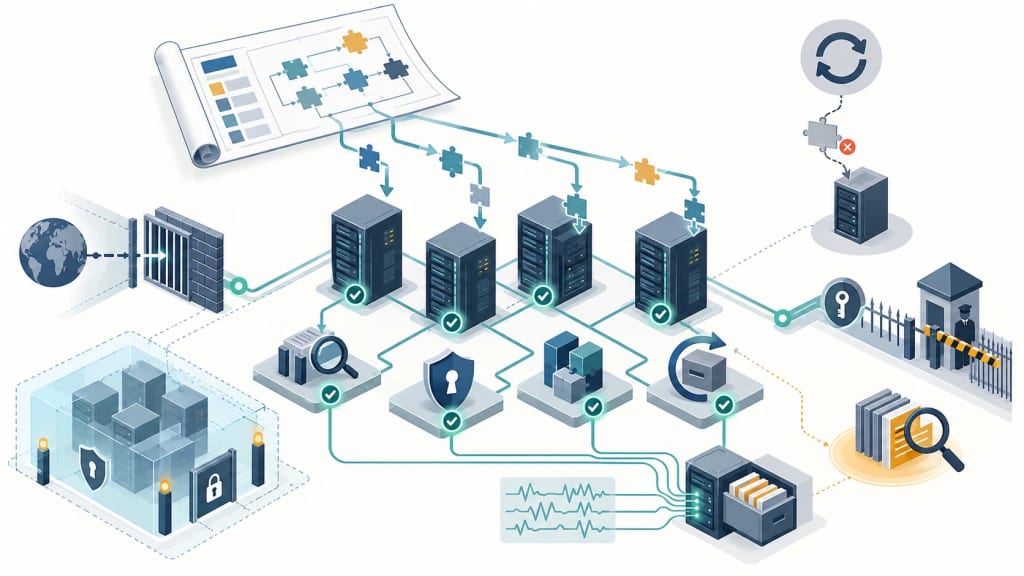
Before closing the ticket, confirm that every SharePoint server and service path is covered. Review external exposure, administrative access, recent authentication and process-creation telemetry, and any unusual file or configuration changes. If the farm cannot be patched immediately, document the vendor mitigation, restrict access as far as the business permits, and preserve relevant logs for investigation.
Practical response checklist
- Identify all SharePoint farms, versions, internet-facing endpoints, and delegated administrators.
- Read the Microsoft advisory for the exact fixed build or mitigation that matches each farm.
- Apply and validate the update in a representative environment, then roll it through production before the CISA date where applicable.
- Review logs for unexpected SharePoint-originated process activity, new accounts, privilege changes, and outbound connections.
- Record the applied build, verification evidence, exceptions, and any follow-up monitoring owner.
Evidence and scope
The CISA catalog is the source for the exploitation listing and September 28 deadline. Microsoft’s Security Response Center is the vendor source for affected products and remediation instructions. Because the advisory page can change as Microsoft adds build details, administrators should re-check it immediately before patching and retain the version information used for the change record.
Try the related loot
Audit OpenClaw Skills for Supply-Chain Risks Before Installing Them